
Documentation
The Four Pillars of Agentic AI Security
A unified control plane for autonomous AI systems
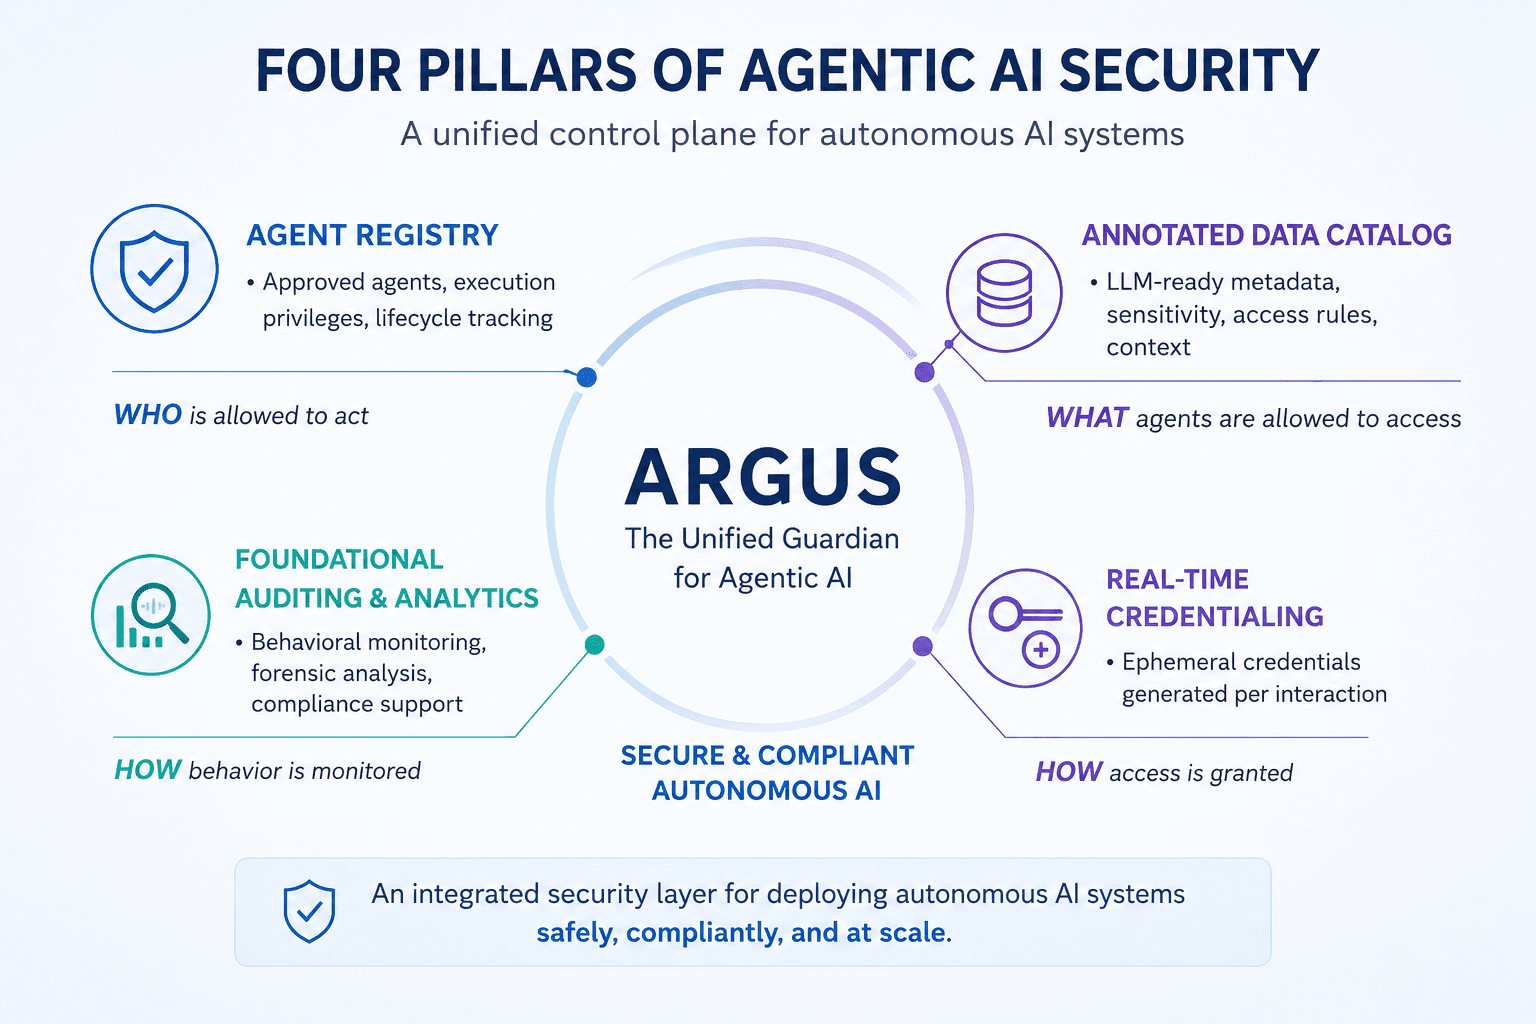
The details
Pillar by pillar
1.
Agent Registry
Who is allowed to act
- Central registry of approved AI agents
- Explicit execution privileges and scope
- Full agent lifecycle tracking (create → run → retire)
Equivalent of IAM — but for agents, not humans.
2.
Annotated Data Catalog
What agents are allowed to access
- LLM-ready metadata: sensitivity, ownership, purpose
- Policy-aware context injection at runtime
- Fine-grained data access enforcement
Turns raw data into governable, AI-safe assets.
3.
Real-Time Credentialing
How access is granted
- Ephemeral, per-interaction credentials
- No standing privileges or hard-coded secrets
- Context-aware authorization at execution time
Zero-trust access for autonomous systems.
4.
Foundational Auditing & Analytics
How behavior is monitored
- Continuous behavioral monitoring
- Full forensic traceability of agent actions
- Compliance-ready audit logs (security, privacy, AI governance)
Makes agents observable, explainable, and defensible.
Bottom line
Together, these pillars form the missing security layer for agentic AI — enabling enterprises to deploy autonomous systems safely, compliantly, and at scale.
Business case
Challenge, and the ROI of closing it
| Pillar | Challenge | What breaks today | ROI / business impact |
|---|---|---|---|
| Agent Registry | “We don’t know what agents exist or what they’re allowed to do.” | Shadow agents, over-privileged bots, no ownership, no kill switch |
|
| Annotated Data Catalog | “We can’t safely expose enterprise data to agents.” | Over-sharing to LLMs, manual data approvals, brittle prompt rules |
|
| Real-Time Credentialing | “Static secrets + agents = inevitable breach.” | Hard-coded tokens, long-lived keys, lateral movement risk |
|
| Foundational Auditing & Analytics | “We can’t explain or prove what agents did.” | No forensic trail, no policy evidence, regulators ahead of security |
|
See the four pillars in action
Get a guided walkthrough of the Argus control plane on your own agents.